Passwordless zero-trust access, automated.
Your customers are still managing shared WiFi passwords and manually offboarding leavers. Staff WiFi fixes all of that with the Purple app, without new hardware.
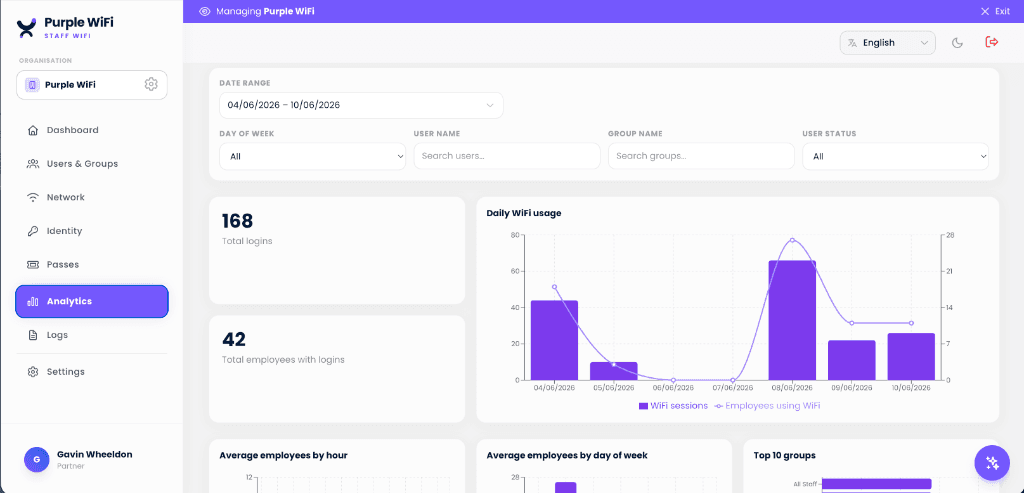
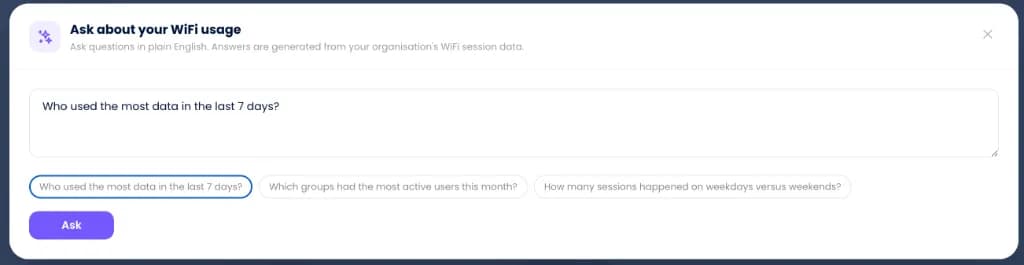
One identity. One pass. Every device, every site.
What your customers get
Staff authenticate once with their existing SSO credentials and get a unique, unshareable certificate-based profile in the app.
Certificate-based authentication. No passwords to share, rotate, or forget.
When a user leaves the IdP, they lose network access automatically. No manual intervention.
Each user gets the right access for their role, automatically, on any device.
Any cloud RADIUS vendor supported. Listed vendors auto-sync.
Zero-touch enrolment through the MDM your customers already run
Purple issues the certificate, your customer's MDM delivers it. 802.1X profiles and EAP-TLS certificates push over SCEP or PKCS to managed devices, so staff join the network without typing anything. Deployments complete in under 30 minutes, with no new hardware to quote.
Microsoft Intune
Windows, macOS, iOS, Android
Your customers deploy certificate-based WiFi profiles over SCEP or PKCS from the Intune console they already use. Compliance state feeds Conditional Access, so a device that fails a rule is refused at authentication.
Jamf Pro
macOS, iOS, iPadOS
Distribute 802.1X profiles and certificates to your customers' Apple hardware through Jamf's SCEP proxy. Devices arrive on the network already trusted - no user prompt, no shared password.
JumpCloud
macOS, Windows, Linux
JumpCloud manages the device and its posture while Purple runs the RADIUS layer. One directory identity governs both the endpoint and its network access, so your customer manages both in one place.
Customer running Kandji, Hexnode, Workspace ONE, or another UEM? Any platform that can deliver a SCEP or PKCS payload enrols devices the same way.
Map a customer's MDM rolloutMicrosoft and Intune are trademarks of the Microsoft group of companies. Jamf and Jamf Pro are trademarks of JAMF Software, LLC. JumpCloud is a trademark of JumpCloud Inc. All are used with permission; this page is not endorsed by or affiliated with them.
Built for identity-first workplaces.
Who your buyer is.
Ready to add Purple to your portfolio?
Join 80,000+ venues already running on Purple. No targets, no minimums, just bigger deals.